
Deadlines are computed, not remembered.
Reviews, contract dates, test dates and incident reports become dated obligations with an owner. Reminders and escalations go out on schedule.
DORA COMPLIANCE PLATFORM
Training, registers, incidents, testing and third parties in one place. Deadlines run themselves. Every step leaves evidence your auditor can verify.
Reviews, contract dates, test dates and incident reports become dated obligations with an owner. Reminders and escalations go out on schedule.
Every export carries its source, extraction time, filters, record count and hash. You hand over a package, not a folder of screenshots.
Reviewed starter risks, assets and obligation templates are there on day one. You confirm and adjust instead of typing from zero.
What is covered
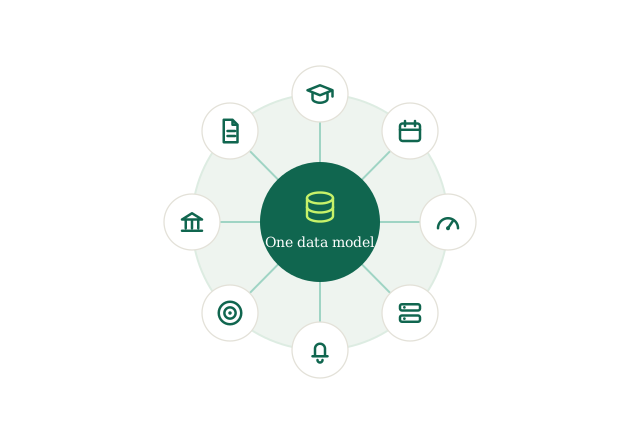
Manage ICT risk, report incidents, test resilience, control third parties, train your people. Dora Check has a module for each, and they share one data model. A provider in the register is the same provider on the incident and on the asset.
TRAINING · DORA ART. 13(6)
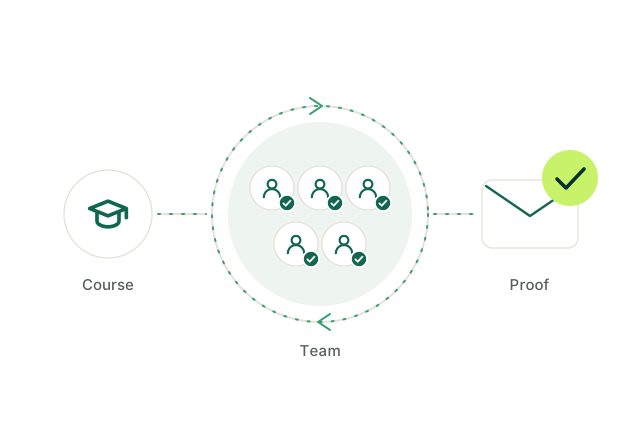
Pick a course and a cycle. Invitations, reminders and the next round run without you. When the last person finishes, the proof record is in your mailbox.
OBLIGATIONS · ALL ARTICLES
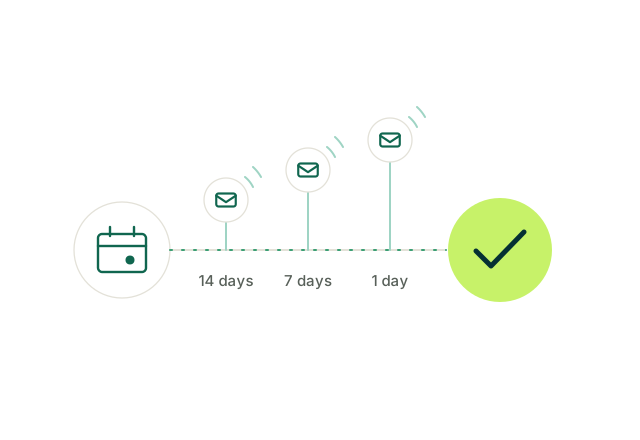
Each recurring duty has an owner, a cadence, a due date and an evidence requirement. Reminders and escalations are sent on schedule, and the log shows that they were.
ICT RISK · DORA ART. 5-16
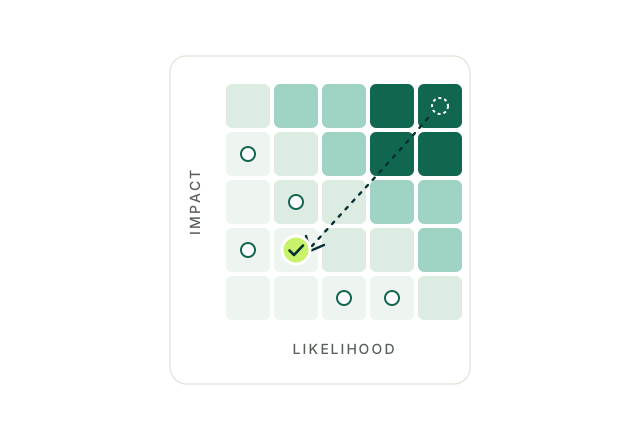
Score each risk by impact and likelihood, attach measures, and see the heatmap. The board report is drafted from the register and waits for your review.
ICT ASSETS · DORA ART. 8
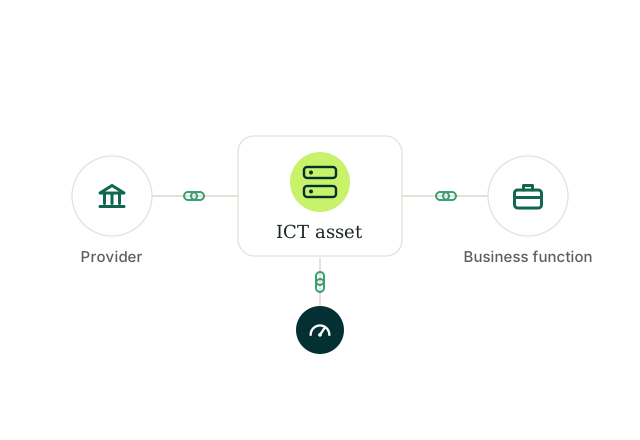
Record each asset with its owner and the business functions it supports. Link it to providers and risks. Import what you already have.
INCIDENTS · DORA ART. 17-23
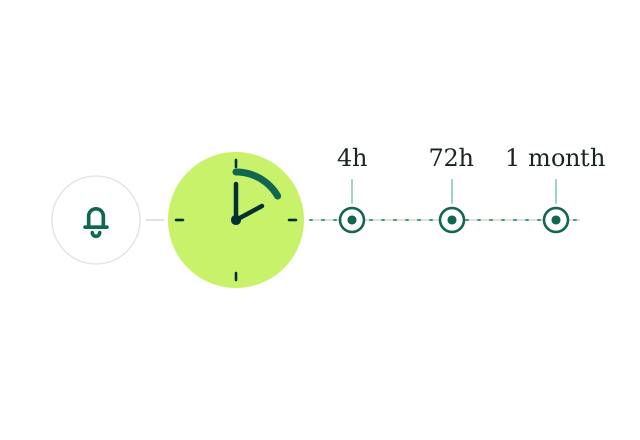
Capture an incident in seconds and classify it with guidance. For a major incident the reporting deadlines are computed to the hour: initial notification, intermediate report after 72 hours, final report after one month.
RESILIENCE TESTING · DORA ART. 24-25
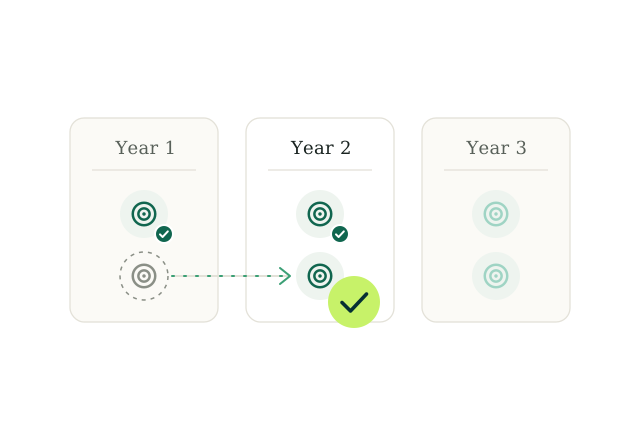
Plan tests across several years and carry over what is unfinished. Management approval is recorded as evidence. A finding stays open until the retest closes it.
THIRD PARTIES · DORA ART. 28-30
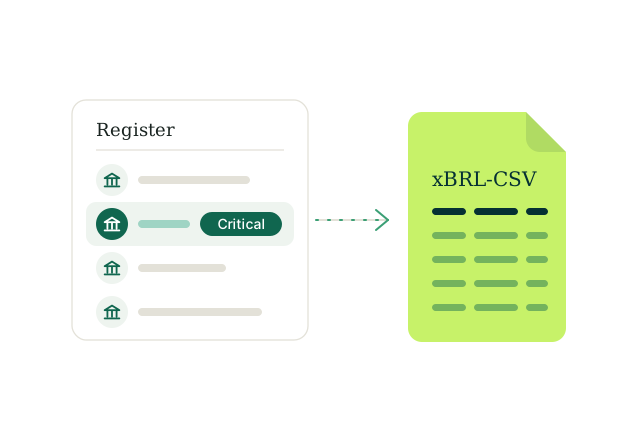
Providers, contracts and criticality in one register. Company data fills in from GLEIF by LEI. Export as xBRL-CSV under ITS (EU) 2024/2956, and import last year's file instead of retyping it.
POLICIES · DORA ART. 5-9
Start from a category catalogue mapped to DORA articles. Approvals and versions are recorded. Reviews are scheduled and end up in the audit package.
AUDIT READINESS
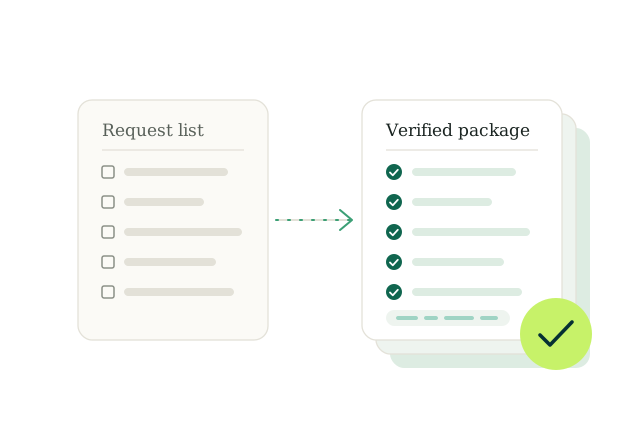
Create the engagement with audit firm, period and reference date. Import the request list as CSV or pasted table. One click builds a verified package from the modules you use; anything else you upload by hand.
COMPLIANCE SCORE
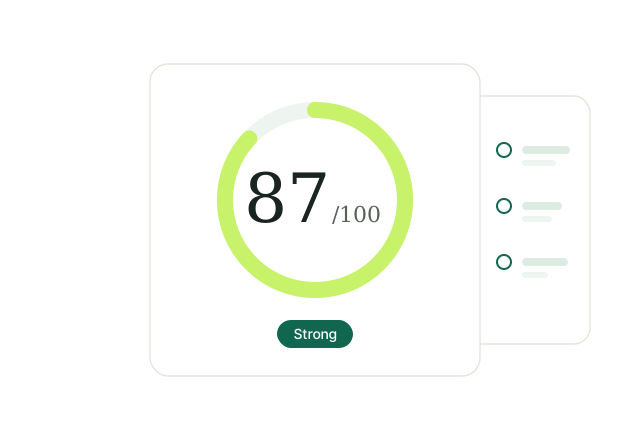
The score is built from every module you use. Open exceptions come first. A weekly summary by email is available if you switch it on.
How it starts
Built for supervised firms
No workspace access without it.
Row-level security on every tenant table, not a filter in application code.
If our staff enter your workspace, access is time-limited and a banner says so.
Hosted in Germany. On request, Dora Check also runs on your own infrastructure.
FAQ
ICT risk management, incident reporting, resilience testing, third-party risk and staff training, plus the obligations calendar and audit evidence that run across all of them.
No. Training and the obligations calendar are the base. You add modules when you need them, and the audit package works with whatever you use.
A verified package per engagement. Every export in it states its source, extraction time, filters, record count and hash.
One sitting. The onboarding asks for your company profile, people, owners and critical functions, then loads starter content.
No. It computes the deadlines, prepares drafts and exports, and records what you submitted and when. You submit.
In Germany. If your policy requires it, we run Dora Check on your own infrastructure.